A few days ago, I wrote about how my side project, vncsnatch, was used by a researcher to accidentally expose the control panels of the Ankara Water and Sewerage Authority (ASKİ) to the Turkish national news.
After the initial panic, the denial from government officials, and the YouTube clickbait, the story has now entered its third and most predictable phase: the lawyers and the infosec community have arrived to debate the ethics of the disclosure.
The conversation in the Turkish cybersecurity sphere has abruptly pivoted from “How could ASKİ leave their water pumps on the public internet?” to “Did the researcher commit a cybercrime by looking at them?”
The Technical-Legal Boundary
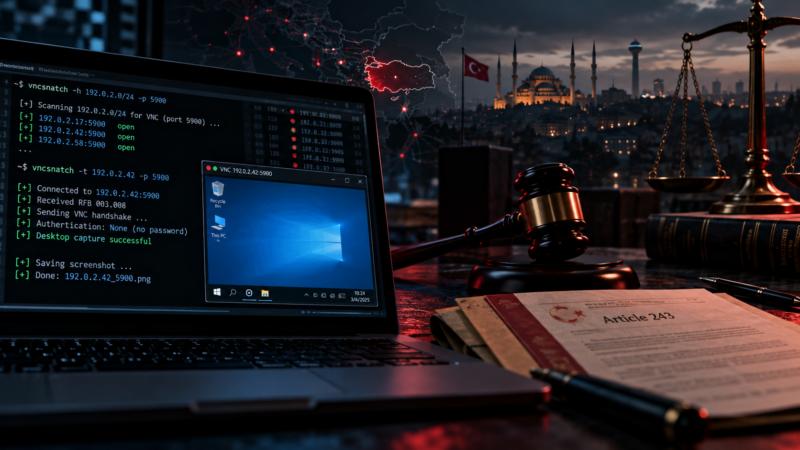
The debate centers around Article 243 of the Turkish Penal Code, which deals with unlawful access to an IT system. To understand why my tool is currently at the center of this debate, you have to understand the mechanics of the VNC protocol and where the line between OSINT (Open Source Intelligence) and active exploitation is drawn.
If you use nmap or Masscan to scan 17 million IP addresses to see if port 5900 (VNC) is open, you are generally in the clear. You are just knocking on doors to see who is home. That is passive scanning. It is the foundation of services like Shodan.
But vncsnatch is designed to go one step further.
When it finds an open port 5900, it initiates the VNC handshake. The server responds with its supported security types. If the server replies with Security Types: None (meaning no password is required), vncsnatch completes the handshake, connects, requests an initial framebuffer update, saves the screenshot to your disk, and severs the connection.
That automated sequence takes less than a second. But legally? That is a massive leap.
The Consensus: A Door Left Open is Still a Door
Independent developers in Turkey (most notably a great technical teardown on iamcanturk.dev) are pointing out that while the water authority’s security posture was negligent, the researcher’s actions were likely illegal.
The consensus is this: The researcher should have stopped at the port scan. They should have noted that port 5900 was open, realized it belonged to state infrastructure, and reported the IP addresses to USOM (Turkey’s national CERT).
By using a tool that actually completes the handshake and pulls down the visual interface of the SCADA system, the researcher technically bypassed the boundary of the system. In the eyes of the law, the fact that the front door was left wide open, with a neon sign pointing to it, does not give you the legal right to step into the living room and take a photograph.
The Messenger’s Dilemma
This puts tools like vncsnatch in a fascinating gray area. I wrote the tool specifically to grab those screenshots because, in my experience as a sysadmin, management ignores spreadsheets of open ports. They only authorize budget for security fixes when you drop a screenshot of an exposed root terminal on their desk.
Visual proof is the only thing that moves the needle. And yet, acquiring that visual proof is the exact moment you cross from a “curious researcher” into an “unauthorized actor.”
If the researcher had just submitted a spreadsheet of IP addresses to the Turkish government, it likely would have been buried in a bureaucratic inbox. ASKİ’s General Manager is currently denying the systems are even theirs despite the photographic evidence. Imagine how easily they would have dismissed a simple port scan report.
The Disclaimer
Building dual-use tools means accepting that people will use them on targets they do not own.
vncsnatch does exactly what I programmed it to do: it acts as a mirror, reflecting the horrific state of internet-facing infrastructure back at the people who configured it. But this incident is a stark reminder to the security community. The technical ease of an action has absolutely no bearing on its legality.
I’ll be adding a fresh, highly visible legal disclaimer to the GitHub repository today. Keep your scans to your own subnets, folks. The law doesn’t care if they forgot to set a password.
Over to you: Where do you draw the line in security research? If a system requires zero authentication to view, should fetching that view still be considered a crime under modern cyber law?