Following the Ankara water leaks, the focus has shifted to the commercial sector. Over the last few weeks, hackers have been systematically thawing out supermarket freezers across France and the rest of Europe. Here is how they are weaponizing HVAC maintenance panels to destroy the cold chain.
2026
31
Oct
When OSINT Becomes a Crime: The vncsnatch Legal Gray Area
The Turkish water infrastructure leak has entered its next predictable phase: debating whether the researcher broke the law. Let’s talk about the exact moment a passive port scan legally becomes unauthorized access, and why vncsnatch sits right on that fault line

28
Oct
When Your Side Project Makes the Evening News in Ankara
I built vncsnatch to demonstrate how many unprotected desktops are sitting on the open internet. Recently, a researcher used it to scan Turkish IP ranges, and accidentally discovered that their critical water infrastructure was one unauthenticated click away from disaster.
11
Oct
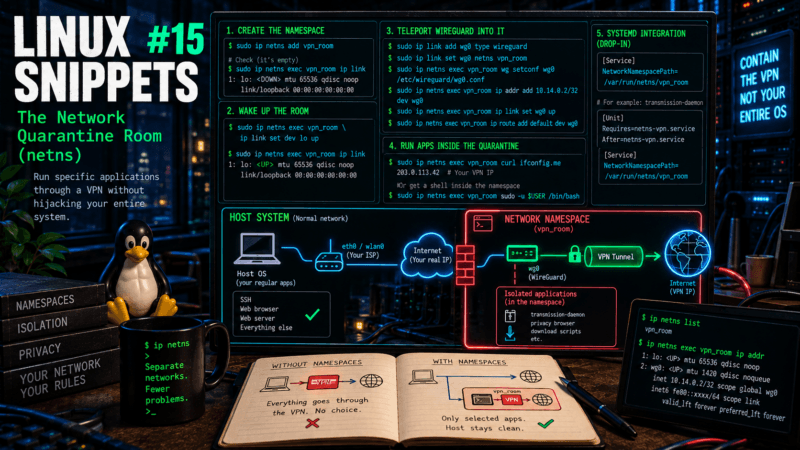
Linux Snippets #15: The Network Quarantine Room (netns)
When you start a commercial VPN client, it brutally hijacks your entire routing table. If you only want to route one specific application through the tunnel while leaving your host untouched, you don’t need a virtual machine – you just need a Linux network namespace.
13
Sep
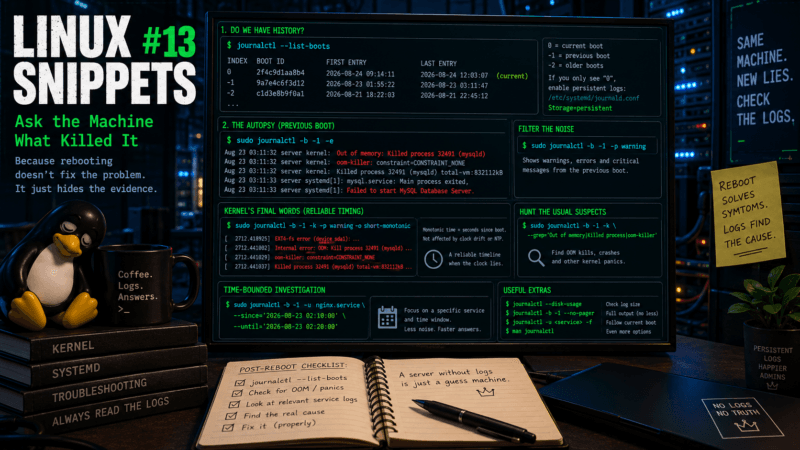
Linux Snippets #13: Ask the Machine What Killed It
After a reboot, every Linux server develops temporary amnesia and insists that everything is running perfectly. Fortunately, the journal may remember the OOM killer, dying disk, or panicking service from five minutes earlier. Here is how to question the previous boot before log rotation provides it with legal representation.
11
Sep

Linux Snippets #12: tcpdump Without Capturing the Entire Internet
Capture everything and inspect it later’ sounds reassuringly forensic until the PCAP consumes the disk, records half the office, and still buries the failed handshake beneath six million irrelevant packets. Here is how to make tcpdump answer one question at a time – with limits established before optimism becomes an incident.
04
Aug
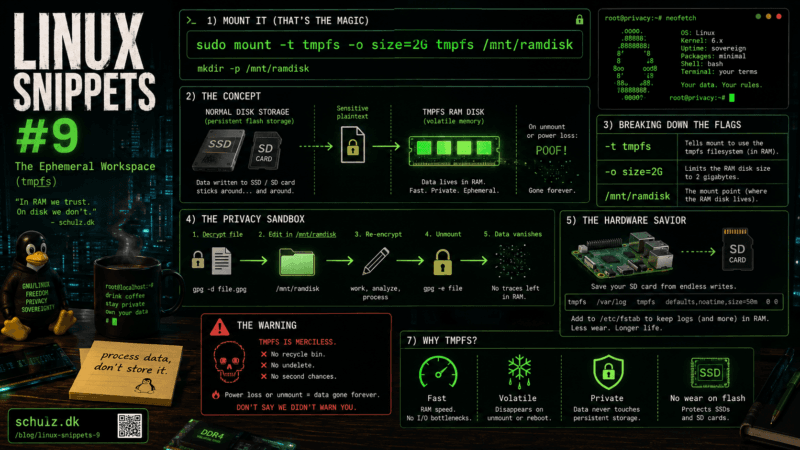
Linux Snippets #9: The Ephemeral Workspace (tmpfs)
Working with highly sensitive plaintext files or trying to stop your Raspberry Pi from burning through SD cards? Here is how to carve out a chunk of your system RAM and mount it as a physical, completely volatile hard drive.
18
May
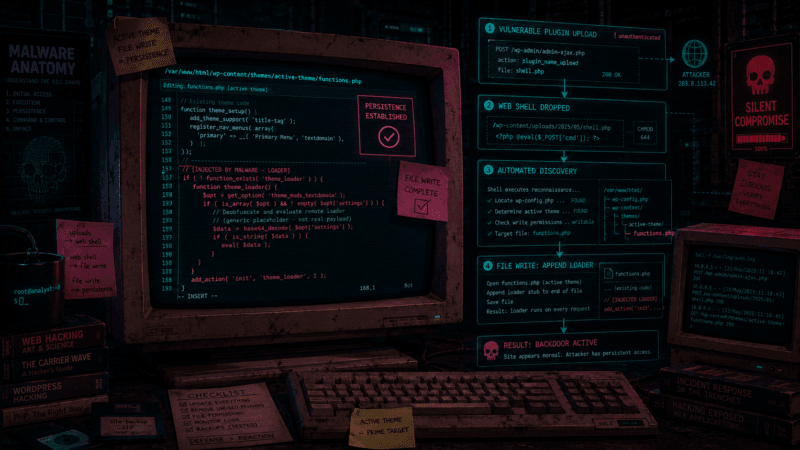
How WordPress Attackers Get Their Dirty Fingers into your System
Most WordPress malware does not begin with a shadowy genius manually editing your theme at midnight. It begins with bots, bored plugins, sloppy permissions, and one unlucky functions.php file that became writable. This is the story of how attackers get the pen, why they keep writing, and why deleting one dirty file is rarely enough.
14
May
The WordPress Backdoor That Forgot to Be PHP
A WordPress backdoor hidden in functions.php is bad enough. One pasted after the closing ?> tag is almost poetic: malware that forgot to become PHP and instead printed its own confession. Here is a technical walk-through of a hidden admin account, query tampering, fake user counts, and the grim beauty of neglected WordPress hygiene.
04
May
Rclone: Zero-Trust Cloud Storage Without the Friction
Stop trusting cloud providers with your personal data. Here is how to use rclone to build a transparent, client-side encryption layer over Dropbox or pCloud