Back in January, I wrote a post titled “When critical infrastructure meets VNC on the open internet.” I published it alongside a small, open-source tool I wrote called vncsnatch.
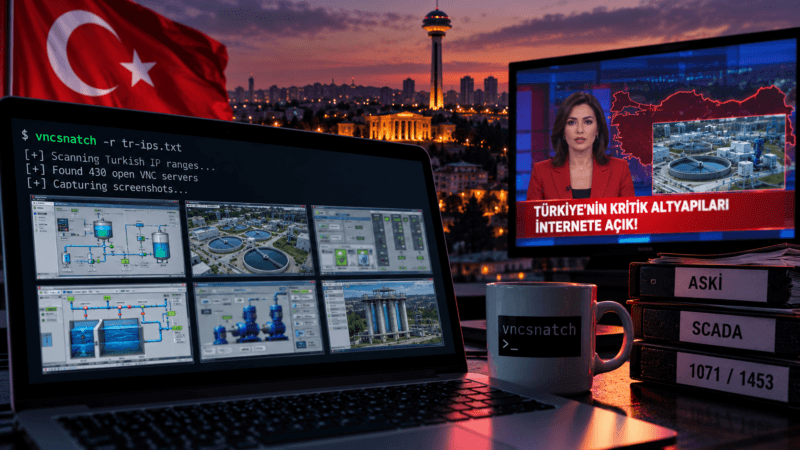
The premise of the tool was simple, arguably primitive: scan a range of IP addresses, look for VNC servers (port 5900) that aren’t protected by a password, and automatically dump a screenshot of whatever is sitting on the screen. I built it because I was tired of explaining to junior sysadmins why binding an unencrypted, unauthenticated remote desktop protocol to 0.0.0.0 is a fireable offense. I figured a folder full of unsolicited screenshots would make the point better than a lecture.
You put a tool like that on GitHub, and you expect a few stars from the OSINT community and maybe some script kiddies. You don’t usually expect it to trigger a national security news cycle in a country you don’t live in.
Issue #1: The Turkish Sweep
Recently, I got pinged on GitHub via Issue #1 on the vncsnatch repository. It turns out an independent security researcher decided to point the tool at a massive database of Turkish IP ranges to see what would fall out of the tree.
What fell out wasn’t just a few neglected Windows 7 machines running point-of-sale software at local bakeries. It was critical national infrastructure.
The story was picked up last week by major Turkish tech outlets like DonanımHaber under the headline: “Türkiye’nin kritik altyapıları internete açık! ASKİ de listede” (Turkey’s critical infrastructures are open to the internet! ASKİ is also on the list).
Water, Sewage, and Unauthenticated Access
For context, ASKİ is the Ankara Water and Sewerage Authority. They manage the water supply and waste management for millions of people in Turkey’s capital.
According to the reports, whoever set up their SCADA (Supervisory Control and Data Acquisition) and remote management systems decided that the most efficient way for engineers to check the fluid levels and pump statuses was to leave a VNC server wide open to the public internet. No VPN. No SSH tunnel. Not even a basic VNC password.
Because vncsnatch is designed to be loud and visual, the researcher didn’t just get a port scan log; they got high-resolution screenshots of the actual industrial control panels regulating the city’s water infrastructure. Anyone with an internet connection and a VNC viewer could have theoretically clicked a button and shut down a municipal water pump.
Update: The “1453” Password Problem
It gets worse. As I am writing this, DonanımHaber just published a follow-up article today.
The researcher kept digging. For the systems that did have a password prompt, they didn’t even need to brute-force them. They just tried “1071” (the date of the Battle of Manzikert) and “1453” (the date of the Conquest of Istanbul). By using these two culturally ubiquitous passwords, they gained access to 430 additional critical infrastructure panels, including more water pumps, wastewater facilities, and valve control systems across various municipalities.
The Messenger’s Dilemma
Whenever an open-source security tool is used to expose a glaring vulnerability, there is a brief moment where people try to blame the tool.
But vncsnatch doesn’t use zero-day exploits. It doesn’t bypass firewalls. It literally just walks up to the front door, turns the handle, and takes a polaroid of the living room. If the door is locked properly, the tool moves on.
The terrifying reality exposed in Turkey isn’t that tools like this exist. It is that in late 2026, state-level infrastructure is still being managed with the security posture of a 1998 home LAN party. We spend millions on next-generation AI threat detection, while the actual control surfaces of our physical world are sitting completely naked on IPv4, protected by a 4-digit historical trivia question, waiting for a bored teenager to stumble across them.
To the sysadmins out there managing our utilities: I beg you, look into SSH tunnels and WireGuard.
Over to you: What is the most terrifying thing you’ve ever seen exposed on Shodan or accidentally discovered on an open port? Let me know in the comments.