A few days ago, we discussed how a simple VNC scanning tool accidentally exposed the unauthenticated control panels of the Ankara Water and Sewerage Authority. That incident highlighted the absurdity of municipal governments plugging critical infrastructure directly into the public internet.
But if you think the private sector is any smarter, I have bad news for your groceries.
Over the last few weeks, a wave of cyberattacks has been quietly sweeping through the European retail sector. It started with a major incident in France where a prominent supermarket chain had their refrigeration systems systematically compromised. Now, copycat attacks are hitting grocery stores and cold-storage warehouses across Sweden, Portugal, Belgium, and beyond.
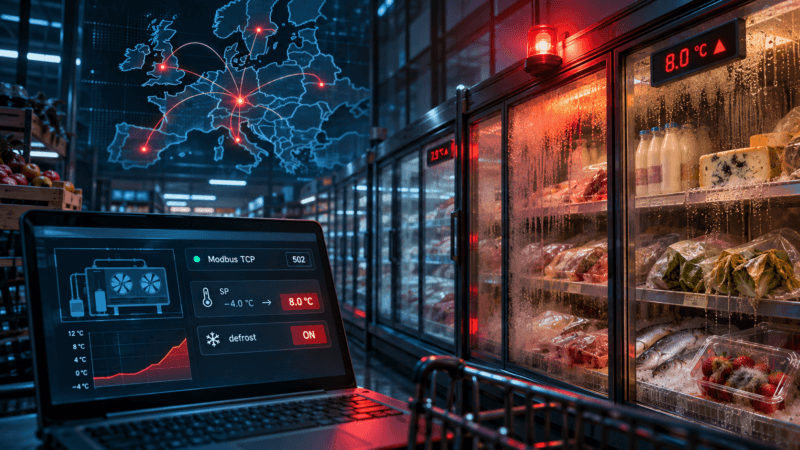
The attackers aren’t stealing credit cards or deploying ransomware. They are simply logging into the store’s climate control systems, turning off the alarms, and forcing the display fridges into a continuous defrost cycle. Temperatures rapidly climb to 50°C (122°F), turning refrigerated cases into ovens.
By the time the morning shift arrives, thousands of euros of perishable inventory have turned into a biological hazard. And the most frustrating part? The attackers are doing it using the exact same negligent attack vector we saw in Turkey.
The Target: The Danfoss System Manager
If you walk into the mechanical room of a modern European supermarket, there is a very high probability you will find a Danfoss AK-SM (System Manager) or a similar localized HVAC/R (Heating, Ventilation, Air Conditioning, and Refrigeration) controller from brands like Copeland or Dixell.
These are incredible pieces of engineering. They regulate the compressors, manage the defrost cycles, optimize energy usage, and monitor the temperature of every single display fridge on the shop floor.
So, how are attackers halfway across the world turning them off?
It all comes down to third-party maintenance. Supermarkets don’t usually employ in-house refrigeration engineers. They contract that work out to regional HVAC companies. And those regional HVAC companies do not want to dispatch a technician in a van at 3:00 AM every time a sensor throws a minor calibration warning.
To solve this, the installation contractor plugs the Danfoss System Manager into the store’s router and forwards a port so they can log in remotely from their office. They bypass the corporate IT department, punch a hole in the firewall, and bridge a piece of critical physical infrastructure directly to the public internet.
The Attack Vector: 1979 Meets 2026
When security researchers started dissecting the French supermarket attacks, they didn’t find sophisticated zero-day exploits. They found open doors. The attacks primarily rely on two glaring vulnerabilities inherent to how these systems are deployed.
Vector 1: The Modbus TCP Problem (Port 502)
Many of these controllers communicate using a protocol called Modbus. Modbus was invented in 1979. It was designed to run over serial cables in physically isolated, locked factory floors.
By design, Modbus has no authentication and no encryption. If you can send a packet to the device, the device will blindly obey the command.
When contractors upgrade these systems to use Modbus TCP (sending the protocol over standard ethernet), they frequently leave Port 502 exposed to the internet. An attacker scanning Shodan for Port 502 can instantly locate these controllers. From there, they don’t need to “hack” anything. They just use a standard Modbus client to write a new value to the holding register that controls the freezer’s temperature setpoint.
The machine receives a perfectly formatted, standard command to warm up the fridge, and it complies.
Vector 2: The “Daily Password” Backdoor (CVE-2025-41450)
If the Modbus port is closed behind a firewall, attackers target the controller’s web management interface.
Recent analysis by Claroty’s Team82 uncovered a breathtakingly negligent design flaw in the web interfaces of Danfoss AK-SM 800 and 800A controllers. The firmware contained an undocumented authentication bypass built around a “daily password.”
To make it easier for support technicians to gain access when a store owner inevitably lost their credentials, the controller maintained a hidden set of master credentials (often using the username admin). The password for this account was not static; instead, the firmware dynamically generated a new password every 24 hours based on a hardcoded mathematical algorithm directly tied to the current calendar date.
Once researchers (and subsequently, threat actors) extracted the firmware and reverse-engineered this date-based math, the entire security model collapsed. To take over a supermarket’s freezer, an attacker no longer needed to brute-force the actual store owner’s password. They simply checked today’s date, ran it through their script to generate the daily token, and logged into the public-facing web panel with absolute, God-mode administrative privileges.
While Danfoss eventually patched this in the newer 800A series firmwares, thousands of stores are still running legacy AK-SM 800 units that reached their official End-of-Life (EOL) years ago and will never receive the fix.
Once inside the web panel, the attacker can initiate manual defrost cycles, shut down the compressors entirely, and critically, disable the email and SMS alert systems. The fridges slowly warm up overnight, and the store manager’s phone never rings to warn them.
The Physical Reality of Digital Negligence
What makes this wave of European freezer attacks so compelling is the visceral nature of the damage.
When a database is breached, the damage is abstract. When a supermarket’s cold chain is broken, the damage is physical, immediate, and incredibly expensive. The store loses its inventory, faces massive disposal fees for the spoiled food, and suffers severe reputational damage.
All of this happens because someone wanted to save a 20-minute drive.
The Solution We Keep Ignoring
This is a solved problem. We have the technology to allow remote maintenance without exposing physical infrastructure to the internet.
If an HVAC technician needs remote access to a supermarket’s refrigeration controller, that controller should sit behind a strictly configured VPN (like WireGuard) or a zero-trust tunnel (like Cloudflare Tunnels or Tailscale). The device should never have a public IP address. It should never be discoverable by a Shodan scanner.
If we don’t start treating the digital boundaries of our physical infrastructure with the same respect we give to our corporate financial data, the script kiddies aren’t just going to leak our passwords—they are going to spoil our food, shut down our water, and literally melt the cold chain.
The Paper Trail (References & Technical Teardowns)
If you want to read the raw data and security bulletins surrounding these specific European attacks, start here:
- Claroty Team82 Research (CVE-2025-41450): Claroty has done extensive teardowns on the Danfoss AK-SM controllers, detailing the date-based authentication bypass vulnerability and the danger of internet-exposed legacy units.
- CERT-FR (French Computer Emergency Response Team): In October 2026, they issued urgent warnings regarding the active exploitation of both Danfoss (AK-SM 800 / AK-SM 800A) and Copeland/Dixell XWEB management devices.
- CISA Advisories: Broader industry alerts have similarly warned about authentication bypasses and command injection flaws on commercial refrigeration units, urging facilities to pull these controllers off the public internet.
Over to you: Have you ever audited the network of a physical retail location? How many undocumented, internet-facing HVAC or point-of-sale systems have you found hiding in the broom closet?