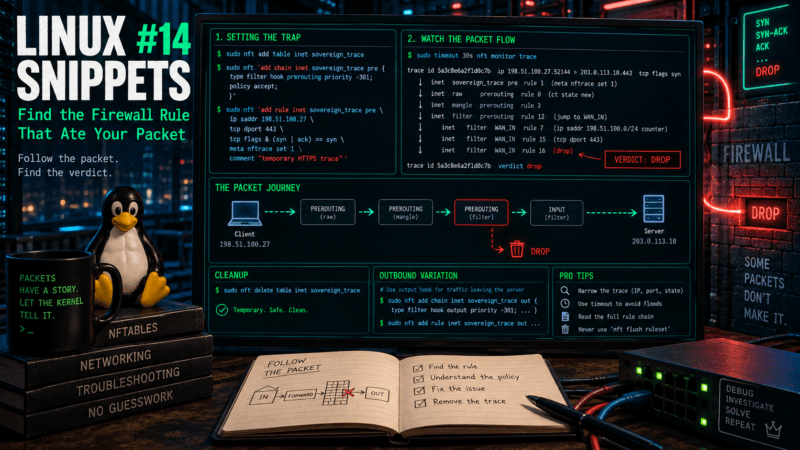
Somewhere inside the firewall, your packet entered a chain, followed three jumps, and was quietly sentenced to death by a rule written during an emergency in 2022. nft monitor trace lets you follow one carefully selected packet through the bureaucracy and discover exactly where policy became homicide.
2026
13
Sep
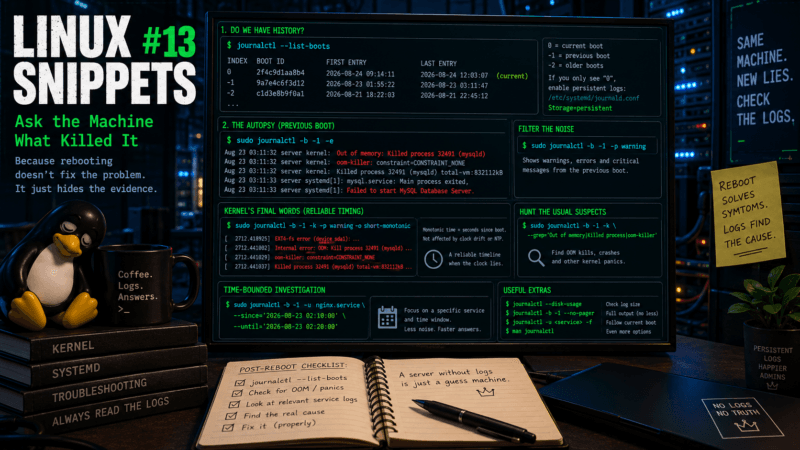
Linux Snippets #13: Ask the Machine What Killed It
After a reboot, every Linux server develops temporary amnesia and insists that everything is running perfectly. Fortunately, the journal may remember the OOM killer, dying disk, or panicking service from five minutes earlier. Here is how to question the previous boot before log rotation provides it with legal representation.
11
Sep

Linux Snippets #12: tcpdump Without Capturing the Entire Internet
Capture everything and inspect it later’ sounds reassuringly forensic until the PCAP consumes the disk, records half the office, and still buries the failed handshake beneath six million irrelevant packets. Here is how to make tcpdump answer one question at a time – with limits established before optimism becomes an incident.
08
Sep
Linux Snippets #11: Run It Once, Contain It, Forget It
Some jobs are too important for nohup, yet far too temporary to deserve permanent accommodation in /etc/systemd/system. Here is how to use systemd-run to give a one-off command strict resource limits, logging, and supervision—and then make the evidence disappear.
18
May
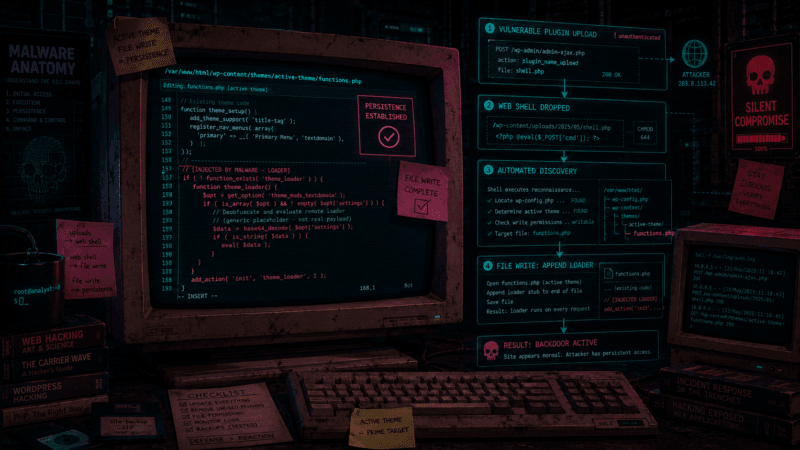
How WordPress Attackers Get Their Dirty Fingers into your System
Most WordPress malware does not begin with a shadowy genius manually editing your theme at midnight. It begins with bots, bored plugins, sloppy permissions, and one unlucky functions.php file that became writable. This is the story of how attackers get the pen, why they keep writing, and why deleting one dirty file is rarely enough.
16
May
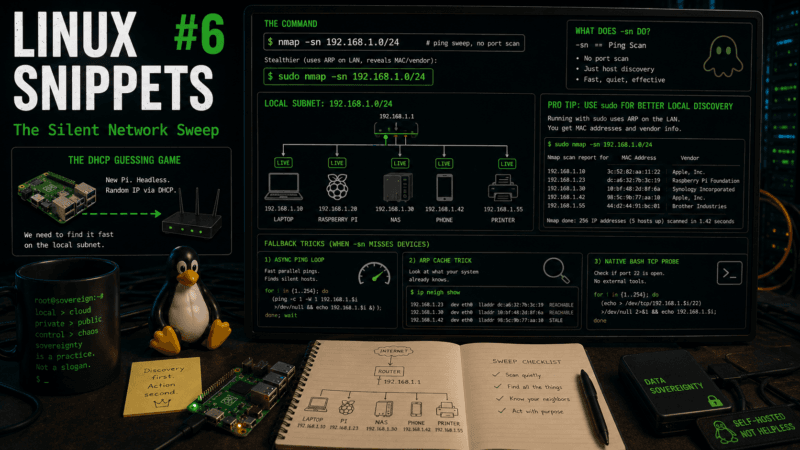
Linux Snippets #6: The Silent Network Sweep
Stop guessing which IP your new Raspberry Pi or IoT device grabbed from the router. Here is the scommand to instantly map your entire local network without triggering alarms
14
May
The WordPress Backdoor That Forgot to Be PHP
A WordPress backdoor hidden in functions.php is bad enough. One pasted after the closing ?> tag is almost poetic: malware that forgot to become PHP and instead printed its own confession. Here is a technical walk-through of a hidden admin account, query tampering, fake user counts, and the grim beauty of neglected WordPress hygiene.
04
May
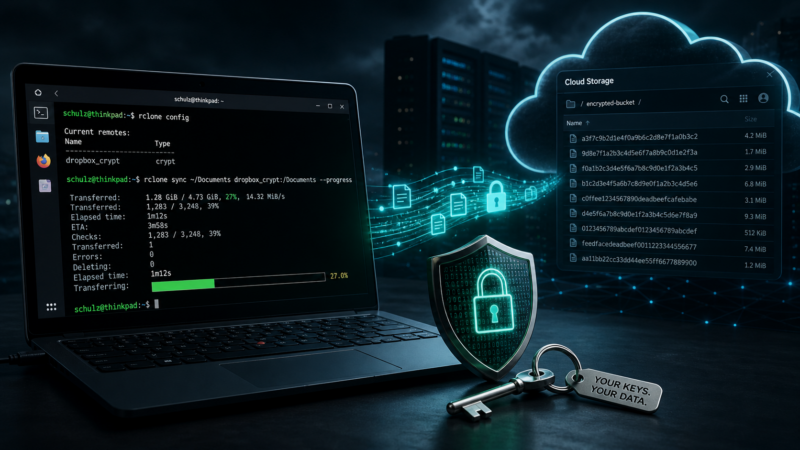
Rclone: Zero-Trust Cloud Storage Without the Friction
Stop trusting cloud providers with your personal data. Here is how to use rclone to build a transparent, client-side encryption layer over Dropbox or pCloud
20
Apr
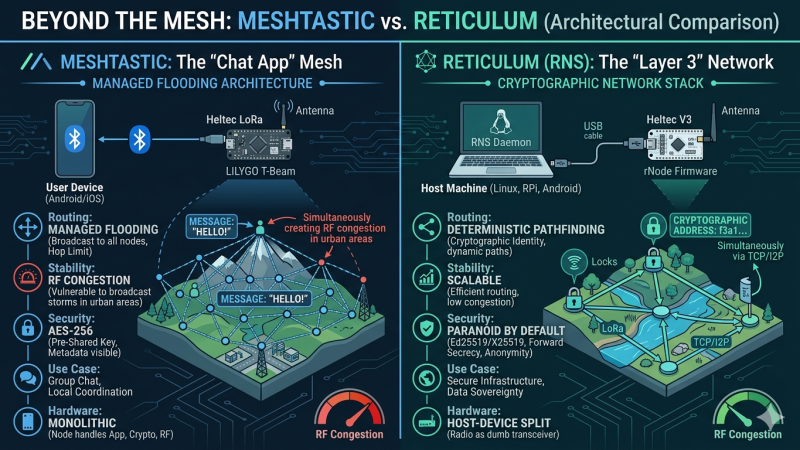
Meshtastic vs Reticulum: Why Reticulum Wins for Scalable Sovereign LoRa Networks
Meshtastic is currently dominating the off-grid communication hype cycle. But when we look under the hood at its managed flooding architecture and symmetric cryptography, does it actually hold up as a foundation for sovereign infrastructure? Here is a deep dive into why I am shifting my focus to the Reticulum Network Stack.
10
Apr
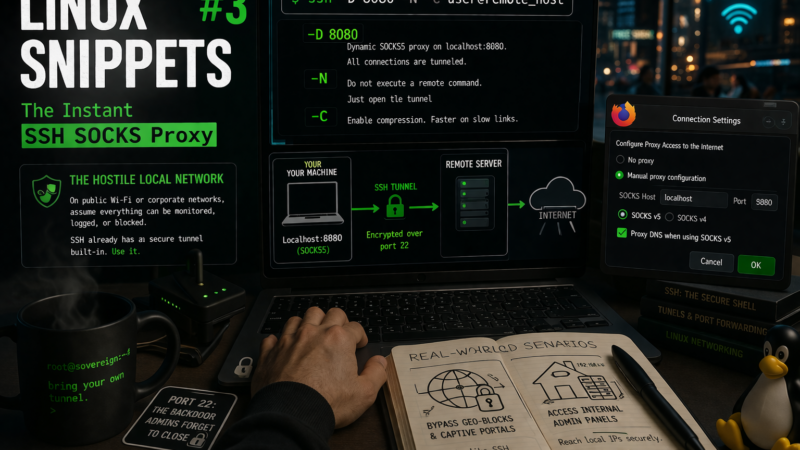
Linux Snippets #3: The Instant SSH SOCKS Proxy
Skip the heavy VPN clients. Here is how to turn any remote Linux server into an encrypted SOCKS5 proxy with a single SSH command to bypass hostile local networks